Who manages Microsoft 365 security baselines in Adelaide?
Subnet does. We are based in Forestville, Adelaide, and use inforcer to apply and maintain an agreed Microsoft 365 policy baseline for South Australian organisations, covering Intune, Entra ID and Microsoft security settings. We assess your tenancy, apply the baseline in stages and tell you when a setting drifts from what was agreed.
What does Subnet use inforcer for?
Subnet uses inforcer as supporting delivery technology for applicable Intune and security-baseline work: applying agreed Intune configuration profiles and security baselines, and helping manage configuration drift. inforcer describes itself as a multi-tenant platform for managed service providers to manage Microsoft 365, and it lists several Microsoft workloads beyond Intune. Subnet’s use of it is limited to what is agreed for your engagement, and some policy work is performed manually instead.
Can we buy inforcer through Subnet, or is it part of +Security?
inforcer is described as supporting delivery technology, not a standalone licence offer and not an automatic +Security entitlement. Whether any licensing, tooling or access is involved, and who holds it, is agreed for each engagement. If you want to understand your options, start with the outcome you need and the Microsoft environment you have today.
What is a policy baseline, and who decides what goes in it?
A baseline is the agreed set of Microsoft policy settings your organisation expects to be in place, reflecting your users, devices and working practices. The settings, the user impact and any exceptions are agreed with you before policy changes are applied. A tool does not decide this: inforcer’s own guidance says it does not decide what your baseline should be, though its templates can be a starting point.
How is an Intune security baseline different from our own policy settings?
Microsoft describes an Intune security baseline as a group of preconfigured Windows security settings, based on recommendations from Microsoft’s security teams and deployed as device configuration profiles. The defaults are mostly the most restrictive values, and Microsoft says Intune cannot know which configuration fits your environment, so it advises understanding the defaults and customising the baseline. Microsoft also notes the baselines are not strictly CIS or NIST compliant. A baseline is a starting point, and the agreed settings should reflect your business.
What is configuration drift, and why does it happen?
Drift is the gap that opens when an environment’s actual settings diverge from its intended baseline. inforcer’s guidance names two common causes: help desk exceptions that are never reverted, and Microsoft platform updates that change defaults. Seeing when a configuration changes is what lets the people responsible decide whether the change was intended, needs an exception or should be corrected.
If a setting changes, is it put back automatically?
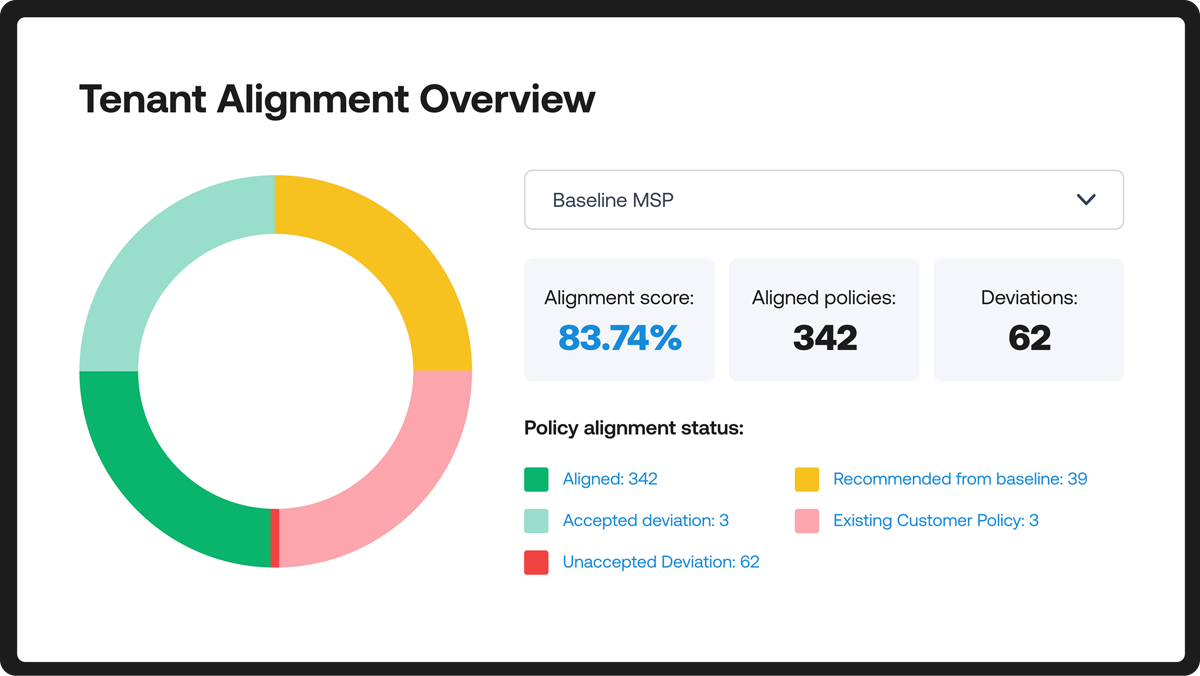
Not necessarily. inforcer can compare tenants with a chosen baseline and alert on deviations, and its own guidance recommends automated detection with human review rather than automatic rollback, because emergency changes and legitimate variations should not be reversed unseen. Who reviews a change, who approves exceptions and who follows up are agreed in scope. A tool’s alerting capability does not by itself mean continuous monitoring or a service level.
If a policy is switched on, does that mean everyone is covered?
No. inforcer’s guidance on this makes the point that a policy being configured is different from it protecting the intended users and devices. Gaps it lists include partial scope, legacy sign-in paths, temporary exclusions that become permanent and service accounts that were overlooked. For that reason, exceptions and exclusions should be agreed, recorded and revisited rather than left in place by default.
How do you avoid a baseline change disrupting staff?
Test before wide rollout. Microsoft notes that a new Intune baseline profile deploys to its assigned groups immediately, so its guidance is to duplicate a profile, assign the copy to a test group, validate the result and then roll out. Duplicates do not carry assignments, so they deploy nowhere until assigned. Microsoft also says changes can take from immediately to a few hours to reach devices, and offline devices update at their next sync, so allow for that when planning and checking.
What happens when Microsoft releases a new baseline version?
Microsoft says existing Intune baseline profiles do not upgrade by themselves. Once a newer version is available, the older profile’s settings become read-only, though names, descriptions and assignments can still be edited. Updating is a choice between keeping your customisations or discarding them. The update creates a side-by-side copy whose assignments must be set again, and settings Microsoft removes keep their last value on devices until something else changes them. Agree who reviews each new version and when.