Skip to content

Technology

Fortinet

Subnet designs, deploys and manages Fortinet networks for South Australian organisations: FortiGate firewalls, Secure SD-WAN between sites, switching and Wi-Fi, and central management through FortiManager.

Network switch and cabling
Fortinet logo

Since 2017

delivering Fortinet projects

750+

Fortinet projects, orders and renewals completed

350+

of those for FortiGate firewalls

20+

FortiSwitch network jobs

WHAT FORTINET OFFERS

One platform for the network and its security

Fortinet builds its firewalls, switches, access points and remote-access tools on one operating system, so they can be run as a single system instead of a set of separate products. These are the parts of the range Subnet works with most.

Firewall

FortiGate next-generation firewalls

FortiGate is Fortinet’s firewall range, from desktop units for a single office to data centre models, with virtual versions for Azure and other clouds. Fortinet builds its own security processors into the hardware so traffic can be inspected, including encrypted traffic, without the slowdown that inspection usually brings. FortiGuard subscriptions add web filtering, intrusion prevention and malware protection.

What it solves

  • A firewall that is out of support or too slow once inspection is switched on
  • One set of security rules across offices, remote sites and cloud networks
  • Visibility of which applications, users and devices are on the network

How Subnet works with it

We size the model against your users, internet links and the security features you will actually enable, then rebuild and test the rule set instead of copying years of clutter across. Cut-overs run in an agreed window with a tested rollback, and high-availability pairs are failover-tested before handover.

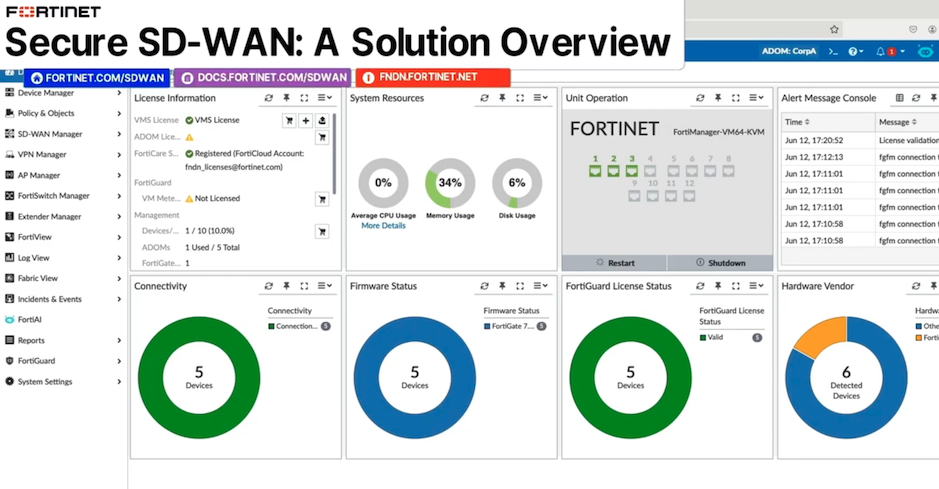
Fortinet SD-WAN management dashboard

Connecting sites

Fortinet Secure SD-WAN

SD-WAN is built into every FortiGate, and Fortinet states it can be enabled on any model without a separate licence. It watches the health of each link (nbn, fibre, 4G or 5G) and steers each application down the one that is performing, failing over automatically when a link drops. Because it runs on the firewall, traffic leaving a branch straight to the internet is still inspected.

What it solves

  • Sites that stop working when their single internet link fails
  • Costly private WAN links carrying traffic that is mostly bound for cloud services
  • Poor call and video quality between sites

How Subnet works with it

We design the link mix for each site, set the performance rules for the applications that matter (voice, Teams, line-of-business systems) and build the secure tunnels between sites. We test failover with you before sign-off, and we have been called in to remediate SD-WAN designs that were not behaving.

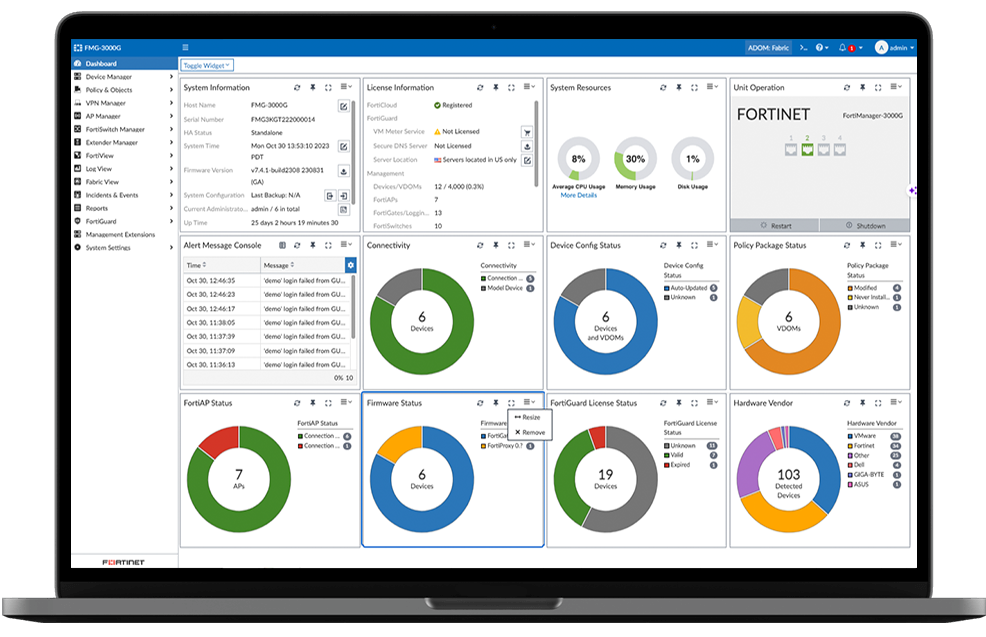
FortiManager network management dashboard

Central management

FortiManager

FortiManager gives one console for every FortiGate, and the switches and access points behind them. Policies, firmware and configuration templates are managed centrally, and new sites can be provisioned from templates without an engineer on site. It is available as an appliance, a virtual machine or FortiManager Cloud.

What it solves

  • Firewalls at different sites drifting apart in configuration and firmware
  • Slow, manual set-up each time a site opens or moves
  • No clear record of who changed what, and when

How Subnet works with it

We deploy FortiManager self-hosted or in the cloud, build templates for each type of site and bring existing FortiGates under management in stages. Under a managed service, we make changes through FortiManager so every site stays on an agreed baseline.

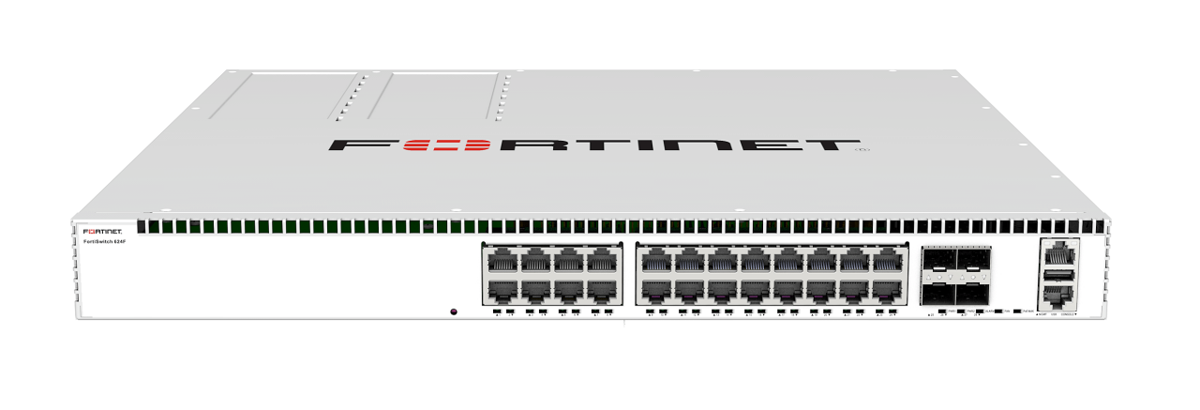
Fortinet FortiSwitch 600 series network switch

Switching and Wi-Fi

FortiSwitch and FortiAP

Fortinet switches and access points are managed from the FortiGate over a link Fortinet calls FortiLink, so they behave as extensions of the firewall. Wired ports and Wi-Fi networks take their security rules from the same place, and Fortinet includes basic network access control for identifying and placing devices as they connect.

What it solves

  • Separate consoles and rule sets for firewall, switches and Wi-Fi
  • Unmanaged ports and shared Wi-Fi passwords
  • Guest, staff and device traffic mixed on one network

How Subnet works with it

We survey the site, design the networks for staff, guests and devices, and replace switching and Wi-Fi in stages to limit disruption. Smaller sites without a FortiGate can be run from Fortinet’s cloud management instead.

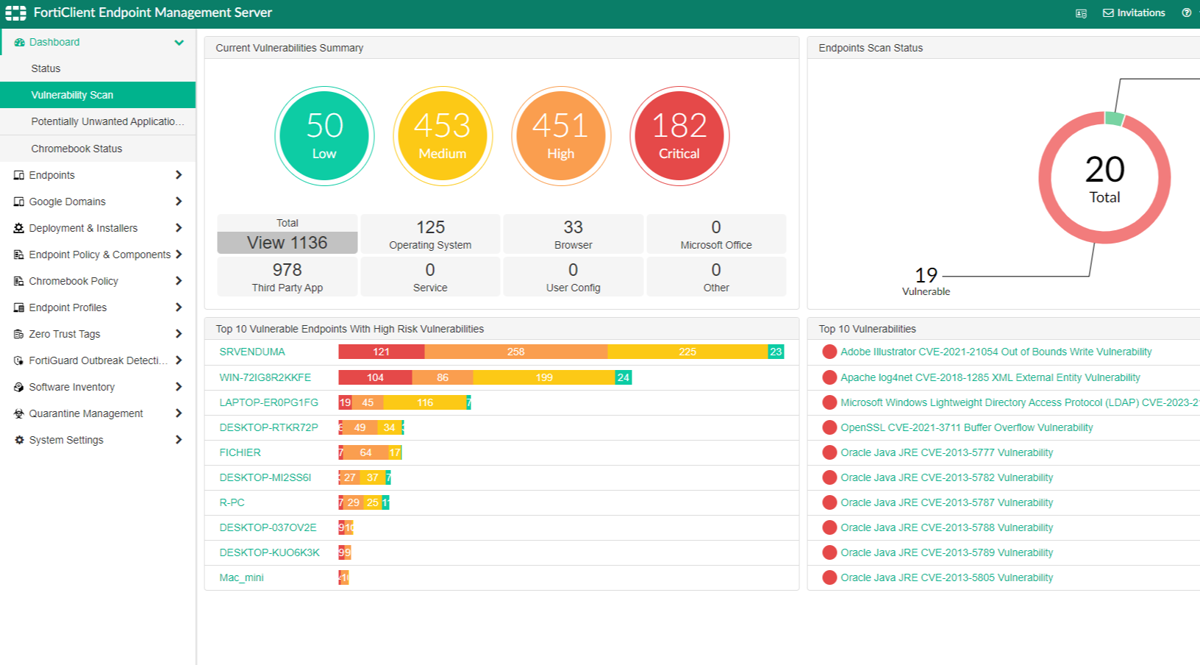
FortiClient EMS vulnerability management dashboard

Remote users

FortiClient, EMS and FortiSASE

FortiClient is Fortinet’s single agent for laptops and mobiles: secure remote access, endpoint protection and vulnerability checks in one install. FortiClient EMS manages those devices centrally, and FortiSASE extends the same protection to people working away from any office.

What it solves

  • Staff who need office systems from home or on the road
  • Checking a device is healthy before it is allowed to connect
  • Replacing an older VPN that everyone complains about

How Subnet works with it

We deploy FortiClient through Microsoft Intune, tie sign-in to Microsoft Entra ID and agree which applications are reachable from where. See secure access and SASE for how this fits a wider design.

Logging and renewals

FortiAnalyzer, FortiGuard and FortiCare

FortiAnalyzer collects logs from FortiGates and FortiClient in one place for reporting and investigation. FortiGuard subscriptions keep the security services current, and FortiCare provides vendor support and firmware. If either lapses, protection and support degrade even though the firewall keeps passing traffic.

What it solves

  • Not having the logs when an incident needs investigating
  • Renewals expiring unnoticed across many serial numbers
  • Evidence for audits and cyber insurance

How Subnet works with it

We set up FortiAnalyzer with sensible retention and scheduled reports, track renewal dates for each device and bring them onto common end dates where that helps. Renewals are the most frequent Fortinet work we do.

WORK WITH SUBNET

How Subnet works with Fortinet

1. Assess

We review what the current network does, what is in and out of support, and what the organisation needs it to do next.

2. Design and size

Models, licences and layout are chosen against real user numbers, links and the features you will enable, with a fixed scope and price.

3. Deploy

Staged build, an agreed change window, acceptance tests signed off by your people and a rollback plan.

4. Manage

Under Managed Services, we look after firmware, changes and monitoring, with FortiManager as the single point of control.

5. Renew and review

We track subscriptions and support for each device and review the design as sites, links and risks change.

WORK WE HAVE COMPLETED

Fortinet projects by sector

Construction

A multi-site FortiGate rollout for a national builder, later extended with virtual FortiGates in Azure and centrally managed licences.

Aged care

FortiGate firewalls and FortiSwitch networks at each new and refurbished site for a multi-site provider, an engagement running since 2017.

Health

A remote-site FortiGate proof of concept configured remotely, followed by FortiManager Cloud for central control.

Environmental services

FortiGates replacing another vendor’s firewalls across sites, a self-hosted FortiManager and SD-WAN remediation.

Education

A full firewall replacement for an independent school, and SD-WAN on FortiGate for a regional school.

Local government and utilities

A firewall migration to FortiGate for a regional water organisation, and depot connectivity over nbn for a regional council.

Resources and related technology

Fortinet's Latest Cyber Strategies

Download Fortinet's free eBook today on Advanced Cybersecurity Strategies.

Download Now

YOUR QUESTIONS

A LITTLE MORE CLARITY.

Who installs and manages Fortinet firewalls in Adelaide and South Australia?

Subnet does. We are based in Forestville, Adelaide, and have designed, installed and managed Fortinet networks for South Australian organisations since 2017, including more than 350 FortiGate projects, orders and renewals. That covers firewall replacement, Secure SD-WAN between sites, FortiSwitch and FortiAP networks and central management through FortiManager. Work can be delivered as a fixed-scope project or looked after under a managed service.

How much does a FortiGate firewall cost?

There are two costs: the hardware, bought once, and the FortiGuard and FortiCare subscriptions, renewed every one, three or five years. The price depends on the model, which is sized to your users and internet links, and on which security services you switch on. Installation and migration are quoted separately as a fixed scope. If you are replacing an older FortiGate, ask about trade-up pricing, and compare one, three and five year terms before deciding.

Is SD-WAN included with a FortiGate, or does it need a separate licence?

SD-WAN is built into FortiGate. Fortinet states it can be enabled on any FortiGate model at no additional cost, and that it can be configured on a single device without other products. What you may still need is a security subscription for the inspection features you want, and FortiManager if several sites are to be managed as one design. The scope should say which links each site uses and how failover is tested.

Do we need FortiManager, and when does it become worthwhile?

Not always. A single FortiGate, or a few, can be managed one at a time. FortiManager becomes worthwhile when several sites need the same policies, firmware and configuration templates, or when new sites must be set up quickly and consistently. It is available as an appliance, a virtual machine or a cloud service. The deciding questions are how many devices you run, how often they change and who is responsible for keeping them aligned.

How long does a FortiGate last before it needs replacing?

Most organisations plan to replace a firewall after five to seven years. The hardware often keeps running longer; what ends is vendor support, firmware updates and the capacity to inspect today’s traffic at speed. Check the end-of-support date for your model, and review sooner if internet speeds, staff numbers or sites have grown since it was installed.

Can FortiGate and other Fortinet renewals be lined up to one date?

Yes. Subscriptions for FortiGates, switches, access points and FortiClient can usually be co-termed so they renew together instead of one serial number at a time. That makes the cost predictable and reduces the chance of a device lapsing unnoticed. Subnet tracks renewal dates for each device and quotes one, three and five year options ahead of the renewal.

What should a FortiGate replacement cover besides the new appliance?

Hardware is only part of it. The scope should also cover the licences and support the new unit needs, how existing policies and settings are carried across or rebuilt, the change window and the handover. It should also say who owns the firewall afterwards. Fortinet’s own migration guidance starts with an audit of what the current firewall does, so unused objects and policies are not carried over by habit.

How should a firewall cut-over be tested and rolled back?

Agree an acceptance test plan before the change window, with someone from each affected area confirming their applications still work. Fortinet’s migration guidance also suggests moving a small group of users first where possible, keeping the old firewall available and having a rollback plan. If the new firewall is a high availability pair, include a failover test. The scope should name the tests, who signs them off and the point at which the team would roll back.

Do we need two FortiGates for high availability?

Only if the business cannot accept the firewall being a single point of failure. A FortiGate high availability cluster uses at least two units that act as one device with a standby ready to take over. Fortinet’s documentation says members of a cluster must be the same model, run the same firmware and have the same hardware configuration, and licences are generally not synchronised between units. The scope should therefore cost two units, their licences and support, plus the switch connections, and test failover.

What happens if FortiGuard or FortiCare lapses?

The firewall keeps routing and its management functions work, but protection and support degrade. According to Fortinet’s technical tip, an expired FortiGuard subscription leaves the FortiGate largely acting as a basic Layer 3 firewall that keeps previously downloaded signatures but loses access to FortiGuard services such as web filtering. When FortiCare support expires, Fortinet assistance and firmware upgrades are lost. Renewal dates are therefore worth tracking for each unit, and the scope should say who tracks them and who applies firmware updates.

BEFORE WE TALK

A useful starting point.

You do not need a finished technical brief. Start with the outcome, what you know today and the questions you need answered.

  • What capability are you looking for?
  • How would it work with your current environment?
  • Who will own licensing, implementation and ongoing operation?
Discuss these priorities

LET’S TALK

WHAT WOULD YOU LIKE TO DO NEXT?

Tell us about your organisation and what you need. Start a conversation, discuss a project or request a meeting.

Prefer to talk?(08) 7127 9400Already a customer and need help? Go to Support.
PROPOSED FORM · PRIVATE PREVIEW ONLY

Preview only. Nothing is sent, stored or booked.

A live version will need final routing, consent and privacy review. Subnet privacy policy

Contact us