Skip to content

Solutions

Secure access and SASE

Subnet designs and manages secure access for South Australian organisations, so people reach the applications they need from any location under one set of rules.

750+

Fortinet engagements since 2017

SD-WAN and remote access

designed, deployed and managed

Netskope and Fortinet

chosen to fit the access problem

WHAT WE DELIVER

Access rules that follow the user

These are the parts Subnet delivers, and the technology we use for each.

Remote access

Zero trust network access

Staff connect to specific applications after their identity and device are checked, instead of joining the whole network through a VPN.

What it solves

  • VPNs that expose more than needed
  • Different tools for different applications
  • Contractors with broad access

How Subnet works with it

We map who needs which application and move groups across in stages.

Web and cloud

Secure web and cloud use

Cloud-delivered security inspects web traffic and shows which cloud and AI services are in use, wherever the person is working.

What it solves

  • No visibility of cloud and AI tools in use
  • Protection that stops at the office firewall
  • Data pasted into unapproved services

How Subnet works with it

We start in monitor mode, review what is found with you and then apply policy.

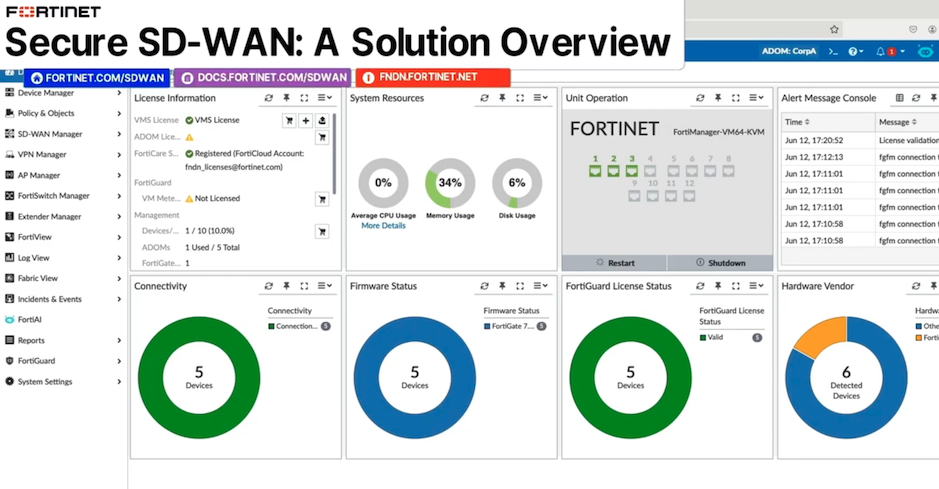
Fortinet SD-WAN management dashboard

Sites

SD-WAN

SD-WAN connects sites over ordinary internet links, steers traffic by application and fails over automatically.

What it solves

  • Costly private links between sites
  • Outages when one link fails
  • Slow access to cloud applications

How Subnet works with it

We design link choices per site and manage the network centrally.

Data

Data protection policies

Policies recognise sensitive information and control where it can be uploaded or shared.

What it solves

  • Sensitive files leaving unnoticed
  • Rules that differ between tools
  • Blocking that gets in the way of work

How Subnet works with it

We agree a small number of clear rules and tune them using real activity.

WORK WITH SUBNET

How a secure access project runs

1. Assess

We map users, applications, sites and current access.

2. Design

The architecture and policies are agreed, with a pilot group.

3. Deploy

Groups and sites move across in stages.

4. Manage

Policies, links and alerts are managed centrally.

5. Review

Access and usage are reviewed and policies adjusted.

SASE, EXPLAINED

ONE ARCHITECTURE. TWO IMPORTANT PARTS.

NETWORKING

SD-WAN

Connectivity and traffic management across branches and sites.

CLOUD-DELIVERED SECURITY

SSE

Web and cloud security, private application access and data controls.

AN ARCHITECTURAL APPROACH

SASE

Networking and security designed to work together.

SSE is the security component of SASE. An SSE deployment alone is not automatically a full SASE implementation.

YOUR QUESTIONS

A LITTLE MORE CLARITY.

Who can design secure remote access and SD-WAN in Adelaide?

Subnet does. We are based in Forestville, Adelaide, and design and manage secure access for South Australian organisations using Fortinet and Netskope. We map who needs which application, pilot with one group, move the rest in stages and manage the policies afterwards.

Do we need to replace our firewalls?

Not necessarily. Your existing environment and requirements determine what can remain and what needs to change. We would scope this before recommending a design.

Is ZTNA the same as a VPN?

Zero Trust Network Access focuses on policy-based access to specific applications. Whether it can replace a particular VPN depends on your applications, devices and operating requirements.

What affects licensing and cost?

The users, locations, products, modules, term and operating responsibilities all affect the scope. Pricing depends on the agreed scope, so it is confirmed once the requirements and the operating model are agreed.

What would Subnet manage?

That is agreed in the statement of work or service schedule. Technology capability does not mean every feature is included in a Subnet service.

Do we need SD-WAN to start with secure access?

Not always. SSE is the security part of SASE, and Microsoft notes that an organisation with networking already in place may find SSE enough. Whether branch connectivity also needs to change depends on your sites, links and applications. Scoping should record which networking and security capabilities are in and out of the work, so an SSE project is not mistaken for a full SASE implementation.

What do a secure web gateway, a CASB and ZTNA each do?

A secure web gateway filters web traffic and blocks unsafe sites and content. A cloud access security broker (CASB) applies data-security policy to the cloud applications people use. Zero trust network access (ZTNA) limits each user to the specific applications they need, after authenticating and authorising them. Together they make up much of SSE, but which ones you need, and how they are combined, is a design decision made during scoping.

How does secure access depend on our identity and device management?

Access decisions are only as good as the signals behind them. Identity platforms such as Microsoft Entra ID can weigh who the user is, the state of the device, the location and the application before allowing access, and the features available depend on the licences you hold. Reviewing identity, device management and licensing early shows what can be reused and what the secure access design must add.

How is a move away from an existing VPN usually staged?

Usually in steps rather than all at once. A common approach is to pilot with a small group, refine the policies, widen the rollout and retire the old access once the new arrangement is working. Which applications move first, how long the two run side by side and who supports users during the change are agreed in the plan for your environment.

Where is our traffic inspected, and does that matter for our obligations?

It depends on the service and its configuration. Cloud-delivered security services process traffic and keep logs in locations set by the provider, so the processing locations, log retention and data-handling terms should be checked during selection. Your obligations remain yours to confirm, and no service by itself guarantees compliance. Subnet can help you ask the right questions and record the answers in the design.

BEFORE WE TALK

A useful starting point.

You do not need a finished technical brief. Start with the outcome, what you know today and the questions you need answered.

  • What outcome matters to your organisation?
  • Which users, applications, systems and risks are involved?
  • What would a practical first step look like?
Discuss these priorities

LET’S TALK

WHAT WOULD YOU LIKE TO DO NEXT?

Tell us about your organisation and what you need. Start a conversation, discuss a project or request a meeting.

Prefer to talk?(08) 7127 9400Already a customer and need help? Go to Support.
PROPOSED FORM · PRIVATE PREVIEW ONLY

Preview only. Nothing is sent, stored or booked.

A live version will need final routing, consent and privacy review. Subnet privacy policy

Contact us